Find articles
23 results for “networking”
GKE API timeouts traced to three bugs across PSC, Envoy, and Linux kernel
A multi-week outage blocking 800 developers across europe-west clusters was caused by packet reordering in Private Service Connect, Envoy half-close behavior, and a Linux kernel bug that silently dropped FIN packets in FIN_WAIT_2 state.
Scale GKE Networking for High-Density AI Agent Workloads with Dataplane V2
GKE Dataplane V2 now handles millions of concurrent AI agent sandboxes by separating identity labels from metadata annotations and filtering high-cardinality labels, enabling sub-second provisioning at 300 sandboxes per second.
Gateway API v1.6 Graduates TCPRoute and UDPRoute to Standard
Gateway API v1.6 promotes TCPRoute and UDPRoute to v1 stability for layer 4 routing, while moving experimental resources like XBackend into a separate API group with X-prefixed names.
The CISO's New Mandate: Governing Autonomous Agents Without Slowing Innovation
As AI agents gain autonomy, CISOs must shift from perimeter defense to identity-centric governance and AI-powered threat detection to secure the agentic enterprise.
CloudFront VPC Origins Go Dual-Stack: IPv6 Without Exposing Origins
AWS adds IPv6 support to CloudFront VPC origins, enabling end-to-end IPv6 delivery to private ALBs, NLBs, and EC2 instances without compromising security.
Configure OAuth for AWS Lambda Kafka Event Source Mappings
AWS Lambda now supports OAuth authentication for self-managed Apache Kafka event source mappings, enabling secure integration with enterprise identity providers like Amazon Cognito or Okta.
GKE ClusterNetworkPolicy introduces tiered enforcement for cluster-wide network security
ClusterNetworkPolicy adds admin, network policy, and baseline tiers to GKE, enabling centralized security guardrails without overriding developer namespace policies.
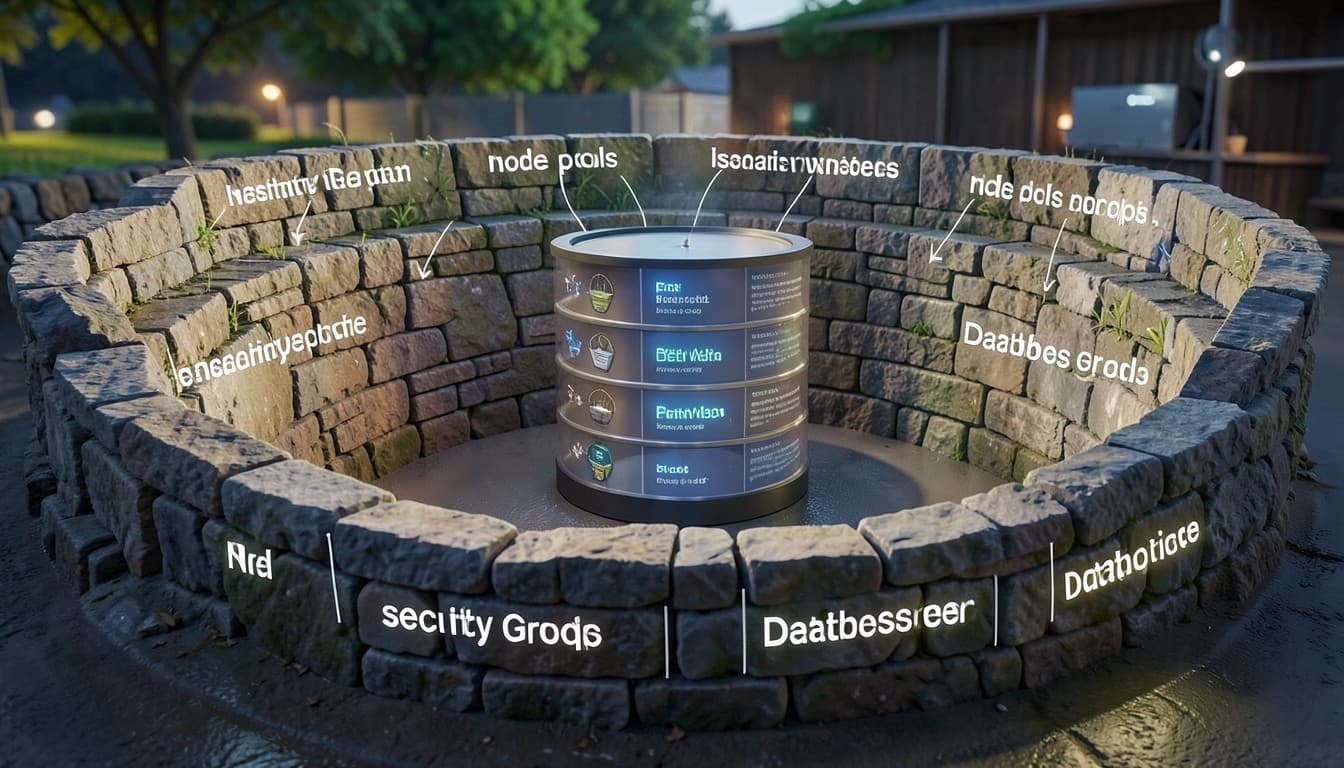
ReadyOn’s Four Walls Model for Tenant Isolation on Amazon EKS
ReadyOn uses four independent layers—Kubernetes namespaces, Karpenter node pools, VPC security groups, and per-tenant Aurora databases—to isolate tenant workloads on EKS for zero-trust security.
Running Multi-Day AZ Evacuation Drills with ARC Zonal Shift
Learn how to run a 48-72 hour Availability Zone evacuation drill using ARC Zonal Shift across ECS, EKS, RDS, and Aurora PostgreSQL with step-by-step CLI commands and observability practices.