Find articles
11 results for “vpc”
CloudFront VPC Origins Go Dual-Stack: IPv6 Without Exposing Origins
AWS adds IPv6 support to CloudFront VPC origins, enabling end-to-end IPv6 delivery to private ALBs, NLBs, and EC2 instances without compromising security.
Route 53 DNS Analytics Turns Query Logs into Actionable CloudWatch Metrics
AWS adds native CloudWatch integration to Route 53 Global Resolver and DNS Firewall, enabling metric filters and alarms on DNS query patterns.
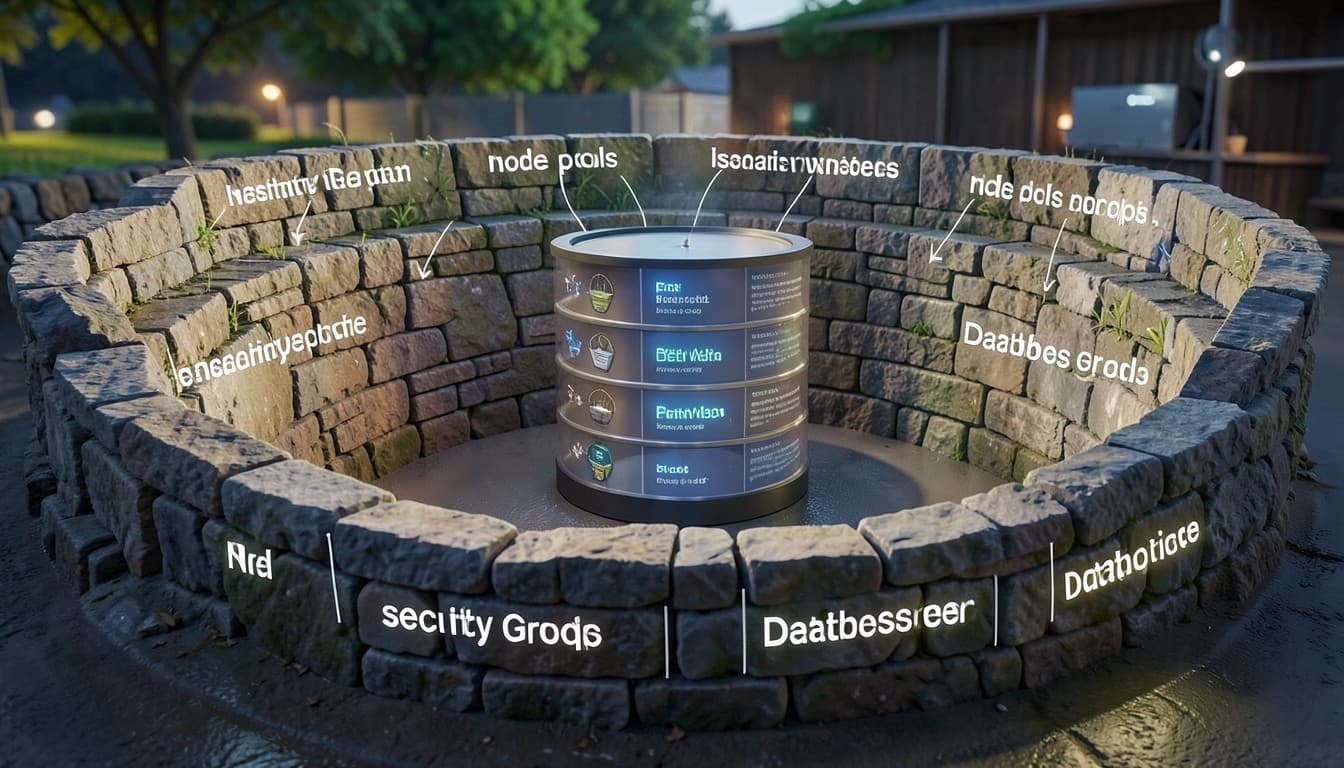
ReadyOn’s Four Walls Model for Tenant Isolation on Amazon EKS
ReadyOn uses four independent layers—Kubernetes namespaces, Karpenter node pools, VPC security groups, and per-tenant Aurora databases—to isolate tenant workloads on EKS for zero-trust security.
How to connect your coding agent to Google Cloud data with Data Agent Kit
Data Agent Kit is now generally available, letting coding agents like Claude Code and Antigravity work directly with BigQuery, Bigtable, and Spark using MCP tools and Google-authored skills.
August 2026 AWS Security Blog Roundup: IAM, GuardDuty, and Compliance Updates
AWS Security Blog published 20 posts in August 2026, with identity and access management leading the month. Key highlights include new IAM policy validation features, GuardDuty malware protection enhancements, and compliance resources for healthcare and financial workloads.
Google Cloud's layered defense against AI abuse, cryptomining, and credential threats
Google Cloud detects emerging threats through infrastructure telemetry and threat intelligence, contains them with granular controls, and provides visibility via abuse logging and Essential Contacts to support customer hardening.
Investigate CloudTrail Events with Natural Language in Amazon Q Console
AWS CloudTrail now integrates with Amazon Q Console, letting you ask plain-language questions about API activity, security events, and operational issues without writing queries.

Encrypt ECS traffic with VPC encryption controls and Service Connect TLS on Fargate
Learn how to enable network-layer encryption via VPC encryption controls and application-layer encryption via Service Connect TLS for Amazon ECS workloads on AWS Fargate, then verify encryption in VPC Flow Logs.

10 questions every startup should answer before moving AI prototypes to production on GCP
Before scaling an AI prototype, startups must answer ten critical questions covering onboarding, scaling, and governance to avoid common pitfalls like leaked keys, quota exhaustion, and uncontrolled costs.